Microsoft Autopilot and Agent Identity: When an Agent Gets an Account
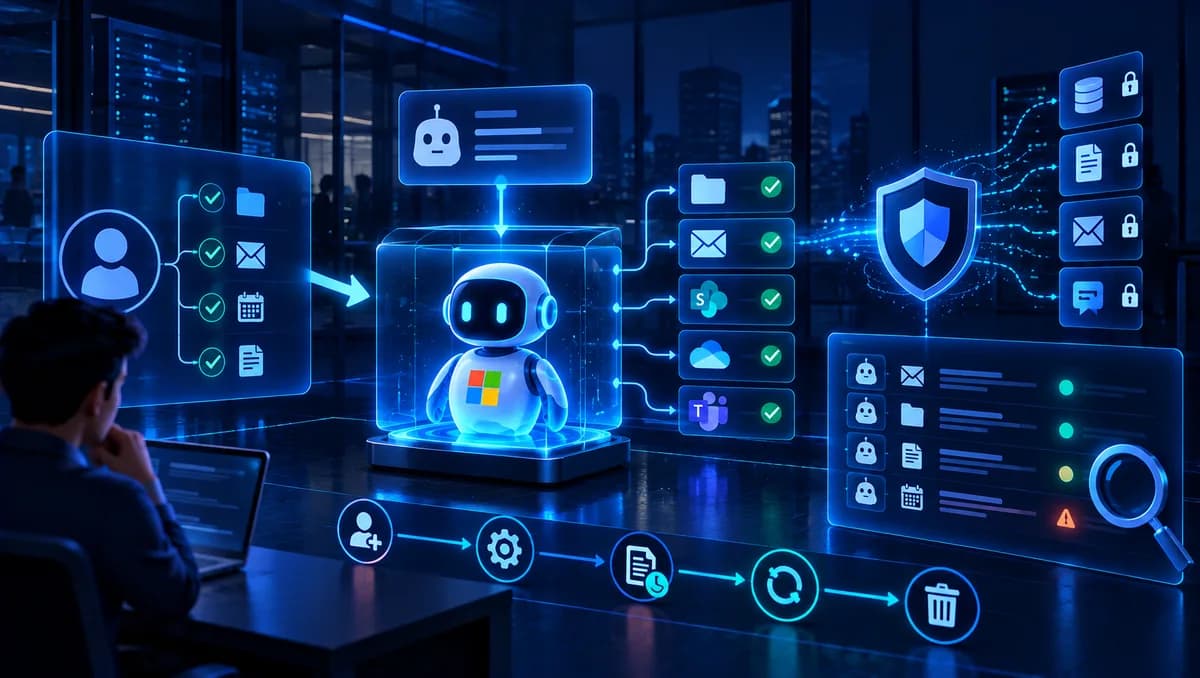
On 25 September, Microsoft renamed its Scout agent Autopilot and placed it alongside Home and Code as one of three modes in a redesigned Copilot app. A user names the agent, gives it a role and a goal, and lets it work: tracking deadlines, compiling project updates, reminding colleagues and gathering material before meetings. The detail that matters most to an enterprise lies in the plumbing. Each Autopilot agent has its own Entra identity, with its own permissions and its own audit log, distinct from any shared service account. Microsoft Autopilot puts agent identity into the directory, and directories come with obligations most organisations have never applied to software.
What Autopilot offers
Autopilot is designed as a persistent colleague more than a chat window. It works towards a goal over days and can reach out to partners on the user's behalf. Microsoft integrates it with Purview for data protection, and sensitive actions can be configured to require a person's approval. Satya Nadella summarised the design intent plainly: "Everything that you observe should be governable by policy."
The commercial model is usage-based. Agent activity consumes Copilot Credits, and spending controls through Agent 365 extend to Autopilot. The product is in restricted testing, and Microsoft has not committed to a date for general availability.

Where the design holds
Giving an agent its own identity is the right call. Agents that act through a shared service account, or through the user's own credentials, leave an audit trail in which nobody can tell what the person did from what the agent did. A distinct identity separates the two, so a security team investigating an action can see exactly which agent took it and under which permissions.
Policy integration matters as much. If the same data-protection rules that apply to employees apply to agents, an organisation does not need a parallel governance system for AI. Configurable approval for sensitive actions puts a person at the point where an error would be expensive, which is where human oversight earns its cost.
Where the enterprise still carries the load
An identity in the directory needs the lifecycle every identity needs. Someone must own each agent and answer for it. Its access should be reviewed periodically, like any employee's. When its owner changes role or leaves, the agent must be reassigned or retired, or the organisation inherits a population of orphaned agents with live permissions and no accountable person. Most identity governance processes were designed for people and service accounts, and few have a place for an agent created by an individual employee in an afternoon.
Least privilege needs deliberate attention. An agent configured by a senior manager could, by default, reach everything that manager can reach. The organisation should decide which permissions agents receive, instead of letting them inherit their creator's access wholesale.
External communication deserves its own policy. An agent that contacts partners on a user's behalf speaks for the company. Which messages require approval, and which partners an agent may contact, are questions for legal and compliance, decided before the agent sends its first email.
Usage-based billing adds a further consideration. Persistent agents working towards goals consume credits continuously, and finance will want budgets and alerts per team before the feature is widely available.
Where it fits
Autopilot suits organisations already standardised on Microsoft 365 that have mature identity governance and can pilot persistent agents in a controlled group. It fits less comfortably where identity processes are informal, because it will multiply the number of identities faster than those processes can absorb. Regulated firms should pilot it with external communication disabled until legal has set the rules.
The broader lesson extends beyond Microsoft. As agents become persistent and act on their own, they belong in the directory, with the same ownership and review disciplines as any account. A CISO should ask how many agent identities the organisation will hold in a year, and who will review each one. An organisation that has answered that before the pilot begins will keep its agents accountable, and its outcomes will survive scrutiny.
Related: Data Architecture
Tell us the number you need to move.
…outcomes that survive scrutiny.